
What Is Social Engineering in Cybercrime?
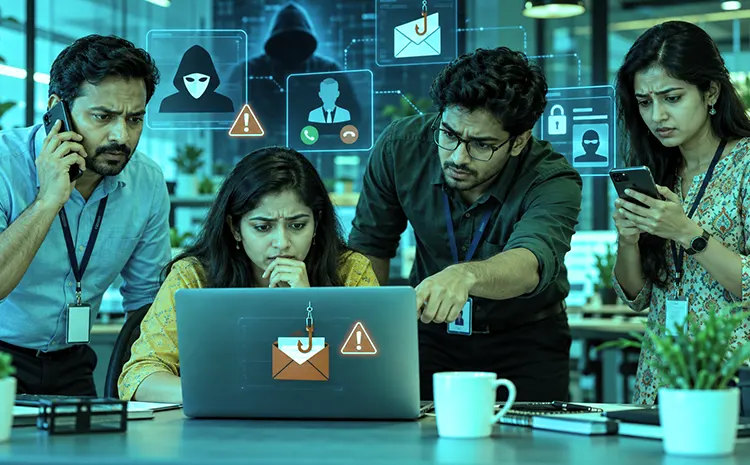
Social engineering is based on manipulation and deception techniques used by cybercriminals to steal people’s confidential information.
Through malicious links included in emails (phishing) and SMS messages (smishing) or through phone calls (vishing), cybercriminals impersonate official bodies, companies and financial entities and report supposed security alerts, bank account anomalies, refunds, outstanding invoices, etc., with the aim of obtaining private information from victims or infecting their devices with malware.
How Social Engineering Attacks Work
The human factor is involved in the vast majority of security breaches caused by social engineering attacks. These attacks aim to gain people’s trust not only to get them to provide their confidential data but also to allow remote access to their devices and download malicious applications or files disguised as legitimate documents and programmes. In other words, they aim to access victims’ devices in a manner similar to a Trojan horse.
This is the case, for example, with cybercriminals who impersonate technical support teams through phone calls, informing victims of a supposed problem or infection on their devices, and claiming they need remote access to install an application to resolve the issue. They may also ask to install another application on the mobile device to take control of it and access all stored information, including SMS messages.
Common Types of Social Engineering Attacks
A social engineering attack is a technique that attackers use to manipulate humans into giving away sensitive information, clicking on malware-laden links, and the like. Here are the most common types:
- Phishing: Malicious emails sent from seemingly legitimate companies to trick recipients into revealing their personal information or to install malware.
- Smishing: People receive fake SMS, and scammers try to get them to click on malicious links or turn over personal data.
- Vishing: Cybercriminals make calls or send voice messages as a representative of a trusted person or organization in order to access sensitive data.
- Pretexting: The attacker develops a fake persona or mission to trick people into giving up information or providing access.
- Impersonation: Attackers impersonate a trusted person, company, bank, or government agency to help establish trust with the victim.
- Baiting: The attacker provides something enticing like a free download or an infected USB flash drive to lure victims in.
Examples of Social Engineering Attacks
Fake Emails and SMS Messages Impersonating Official Organizations
For years, cybercriminals have used fake emails and SMS texts to target users by claiming they were from government agencies, tax offices or private companies to convince people to click and execute a malicious download. Examples include fake content for unpaid fines, tax return documents and submission requests. Some of the pretexts used have included alleged unpaid fines or documents pending submission to the Tax Agency.
Tips to Prevent Social Engineering Attacks
- Avoid Suspicious Links and Attachments: Do not provide personal or banking information on websites accessed through links in suspicious emails or text messages. Do not download attachments from these types of communications either.
- Check the Sender’s Identity: Carefully check the sender of emails, and do not take any action if you verify that it is not the official sender. As a general rule, no company or public body will request personal or sensitive information from you through these channels.
- Visit Official Websites Directly: It is always preferable to access a website by typing the address into the browser, not through links.
- Be Careful with Urgent or Alarming Messages: Be wary of all alarming emails and messages that have an urgent tone, contain spelling mistakes or typos, and are not addressed to you personally.
- Verify Suspicious Phone Calls: If you receive a call that makes you doubt its legitimacy, do not take any action and contact the company directly (by searching for the phone number online or on their official website). Block fraudulent phone numbers so they cannot call you again.
How to Recognize a Bank Impersonation Scams
BBVA will never ask for your confidential information, such as online banking passwords or one-time passwords (OTPs), via SMS messages, emails, or calls initiated by the bank. Remember that BBVA SMS messages do not contain links; if you receive one that includes a link, even if it appears in a BBVA thread, it is fake. Likewise, if you receive a call requesting this information, even if you see the bank’s official number on your screen, do not provide it. Cybercriminals are using techniques to manipulate it.
Strengthen Device Security to Prevent Social Engineering
- Strengthen the security of your devices and keep your operating system, browser, and applications up to date. Also, install antivirus software and run regular scans.
- Download apps from official app stores like Google Play or the App Store, and check if the app has been downloaded by a large number of users, has a high rating, and has positive reviews. These indicators help you recognise the app’s authenticity.
Conclusion
Social engineering is a tactic that targets human trust to manipulate an individual into giving out information, distributing malware, or breaching computer systems. Be aware of the warning signs, verify requests, never click on links you are unfamiliar with, and be cautious when giving out personal information to keep yourself safe from these types of attacks.
Continue Reading: