
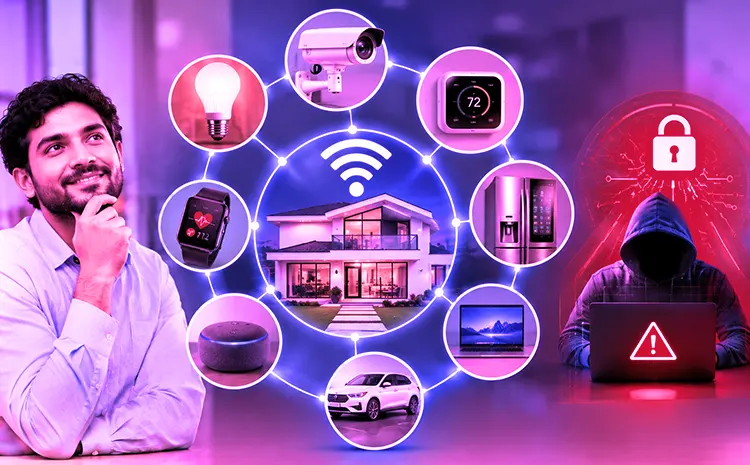
The Internet of Things (IoT) refers to a network of physical devices connected to the internet that collect, share, and exchange data. We’re talking about things like smart cameras, routers, sensors, and even wearable technology like smartwatches. These devices can share and exchange data with each other, which makes our lives easier and helps businesses run more smoothly. But there’s a downside—if we don’t keep these devices safe and secure, they can pose a risk to our security. This is because they can be hacked or compromised if we’re not careful. So, it’s critical to manage and protect our connected devices properly.
How Does the Internet of Things Work?
The Internet of Things (IoT) is a collective term for technologies that form a global infrastructure in information societies. The IoT enables physical and virtual objects to network and collaborate through information and communication technologies.
At the same time, the technologies of the “everything network” allow interaction between people and networked electronic systems. But networked systems can also interact with each other, thus supporting people in their activities. They should neither disturb nor distract nor be conspicuous. For example, miniaturized computers, so-called wearables, with various sensors are being integrated directly into clothing.
The Internet of Things (IoT) therefore refers to the linking of uniquely identifiable physical objects (things) with a virtual representation in an internet-like structure. This in turn means that it consists not only of human participants but also of things.
What Does the Survey Reveal About IoT Security Risks?
But why don’t companies apply compliance rules when it comes to Internet of Things (IoT) technologies? A survey sheds light on this: Smart devices such as routers, VoIP phones, network cameras, Wi-Fi access points, and IoT devices in production are ubiquitous. Nevertheless, the security risks they pose are often underestimated. The security specialist IoT inspector reached this conclusion. They conducted a survey of representatives from companies of different sizes. The survey focused on how businesses assess the security risks of smart devices and the protective measures they use to mitigate those risks.
Also Read: Digital Security Challenges With The Internet Of Things
Lack of Clarity Regarding IoT Security Responsibilities
When it comes to security for internet-connected devices, a lot of companies are unclear about who’s in charge. This is a big part of why many of them don’t have rules in place for these devices. In some companies, the Chief Technology Officer or Chief Information Officer is responsible, while in others it’s the procurement department or outside experts. But it’s really important to know who’s responsible for keeping these devices secure, so companies can manage risks and make sure their devices are following the company’s security rules. This way, they can protect themselves from potential problems.
85 percent of the surveyed decision-makers agree that cybercriminals have already targeted smart devices. Servers, computers, and Industry 4.0 systems are considered particularly vulnerable. Only 28 percent see network-connected medical technology and just 14 percent IP telephony as being at risk.
But every IoT device is susceptible to manipulation and not protected against cyberattacks. The IoT Inspector warns against a lack of risk awareness: “That’s a gross miscalculation that may have been valid ten years ago. Today, every device—from routers to video conferencing systems to keyless entry systems—is a Trojan horse for attacks on companies and organizations.”
What Are the Key Security Factors in the Internet of Things?
Since IoT devices have a unique identity and are interconnected via the internet, the risk of cyberattacks or misuse by unauthorized third parties is a real concern. To minimize these risks, it is crucial to secure communication between IoT devices. This prevents manipulation of processes and workflows, ensuring the protection of internal company data. The following security factors should be considered:
- Effective and reliable identity and access management
- Encryption of all data transmitted over the internet
- Firewalls to protect individual systems
- Effective hardening of systems to reduce the attack surface
- Software and patch management throughout the entire operating life of the systems
Common IoT Security Risks and Protection Measures
Some common IoT security risks and the measures organizations can take to address them include,
| IoT security risk | Potential impact | Protection measure |
| Weak passwords | Unauthorized access to connected devices | Use strong, unique passwords |
| Unencrypted communication | Exposure of sensitive data | Encrypt data transmitted between devices |
| Outdated software | Exploitation of known vulnerabilities | Apply regular software updates and security patches |
| Poor access management | Unauthorized users gaining device access | Use identity and access management |
| Insecure network connections | Attackers accessing connected systems | Use firewalls and network segmentation |
| Lack of monitoring | Delayed detection of suspicious activity | Monitor device activity and network traffic |
By taking these aspects into account when building the Internet of Things and its individual systems, we can already minimize the attack possibilities for cybercriminals.
What IoT Security Vulnerabilities Did Microsoft Researchers Discover?
Microsoft researchers have discovered extensive memory errors in the code used for IoT devices. This makes the systems more vulnerable to cybercriminals, who can more easily inject and execute malicious code. Vulnerable products include Samsung Tizen, Google Cloud, Amazon, Red Hat, ARM, and Texas Instruments. However, not all devices are affected equally; the vulnerabilities vary in severity. For example, Samsung Tizen scores 3.2 out of a possible 10 points, while a Red Hat product scores 9.8 points, indicating a significantly higher risk.
Microsoft, in cooperation with the US Department of Homeland Security, notified the affected manufacturers of the vulnerabilities. A list of all vulnerable products can be found in the Microsoft security advisory. For better protection, Microsoft also recommends patch management, the use of a VPN with two-factor authentication, network segmentation, and firewalls.